Q-Day is the day a quantum computer becomes powerful enough to break the public-key encryption that protects most of the internet, such as RSA and elliptic-curve cryptography. It has not happened, and nobody knows when it will: published forecasts range from 2029 (Gartner) to the late 2030s, and the NSA says it "does not know".
This page explains what Q-Day means, what breaks and what does not, why it matters before it happens, and what you can do. Every figure links to its source.
What Q-Day means
The "Q" stands for quantum. Experts call the machine that could do it a cryptographically relevant quantum computer, or CRQC. No such machine exists today.
Most online security rests on math problems that ordinary computers cannot solve in any useful time. RSA, for example, relies on how hard it is to split a very large number into its two prime factors. A quantum computer running Shor's algorithm could solve exactly this kind of problem. Think of a lock that is safe because picking it would take a burglar a million years. Q-Day is the day someone builds a tool that opens it in a week.
What breaks, and what does not
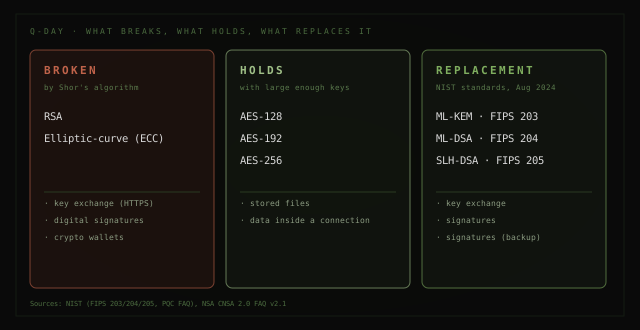
Q-Day does not break all encryption. It breaks one family: public-key cryptography, the part that sets up a secure connection and proves who you are.
RSA: broken. RSA protects key exchange and digital signatures, for example on websites and software updates. Shor's algorithm finds the prime factors RSA depends on.
Elliptic-curve cryptography (ECC): broken. ECC does the same job with shorter keys, and Shor's algorithm breaks it too. Google notes that "most blockchain technologies and cryptocurrencies currently rely on" this kind of cryptography (March 2026). A Google Quantum AI team estimated that the 256-bit elliptic curve used by cryptocurrencies could be broken in "minutes" with fewer than half a million physical qubits (2026 paper). What that means for your coins is in our Bitcoin explainer.
Symmetric encryption such as AES: holds. This is the encryption that scrambles the data itself once a connection is set up, or a file on disk. Quantum computers help much less here. NIST writes that "AES 128 will remain secure for decades to come", and that current applications can keep using AES with 128, 192 or 256-bit keys (NIST FAQ). The NSA calls symmetric algorithms "secure, provided the key size is sufficiently large" (CNSA 2.0 FAQ).
Why it matters before Q-Day
An attacker does not need a quantum computer today to benefit from one later. Encrypted traffic can be recorded now and stored until it can be decrypted. This is called harvest now, decrypt later. The US government names this risk in Executive Order 14412 (June 2026): adversaries collecting US information now, to decrypt it once large quantum computers work.
Data that must stay secret for many years, such as medical records or state secrets, is therefore already at risk, whatever the exact date of Q-Day.
When is Q-Day?
Nobody knows. These are the main published forecasts, each with who makes it:
2029: Gartner expects quantum computers to "break public key cryptographic algorithms" (February 2025; only the public summary is readable).
April 2030: the Cloud Security Alliance set a countdown clock in 2022 to the day quantum computers could break "present-day cybersecurity infrastructure".
November 2033: the median of Metaculus forecasters for factoring the RSA-2048 challenge number (26 forecasters, measured 9 October 2026).
Around 2035 and 2040: in a Global Risk Institute survey of 26 experts, the chance of a quantum computer that breaks RSA-2048 within 24 hours is 28–49% within 10 years and 51–70% within 15 years (report March 2026).
No date: the NSA writes: "NSA does not know when there will be a CRQC."
Our Q-Day countdown runs to the earliest of these published estimates. The Q-Day tracker keeps every forecast with its source, and we update it when one moves. Government migration deadlines, such as 2035 for US national security systems, are not forecasts. We list them in who must do what, and when.
How far away is it?
The most cited estimate is by Craig Gidney of Google Quantum AI (May 2025): RSA-2048 could be broken with fewer than one million physical qubits in less than a week. Today's qubits make too many errors, so many physical qubits must work together as one reliable logical qubit. Gidney's machine works with about 1,400 logical qubits.
A benchmark by Sandia National Laboratories, with Quantinuum and NVIDIA (September 2026), ran up to 8 logical qubits on Quantinuum's Helios-1. The authors write that today's machines are "insufficient by roughly five orders of magnitude" for RSA-2048. At the same time, the target keeps shrinking: in 2019 the estimate was 20 million physical qubits. We explain the numbers in how many qubits it takes to break RSA-2048.
What we do not know
We do not know whether hardware will keep improving at its current pace, or whether a new algorithm will lower the target again. Forecasts can move in both directions. Anyone who gives you an exact date for Q-Day is guessing; that is why we always say who makes a forecast.
What you can do
The fix exists. In August 2024 NIST published its first three post-quantum standards: FIPS 203 (ML-KEM) for key exchange, and FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA) for digital signatures. NIST urges organizations to "begin transitioning to the new standards as soon as possible". More in post-quantum cryptography explained.
As an individual: keep your browser, operating system and apps up to date. Quantum-safe encryption reaches you through software updates. If you hold cryptocurrency, check how your address type is exposed.
As an organization: start with an inventory of where you use RSA and ECC. The UK's NCSC sets three milestones: discovery and a migration plan by 2028, the highest-priority migrations by 2031, and all systems migrated by 2035. Our practical guide walks through the steps.
Frequently asked questions
Has Q-Day already happened? No. No quantum computer has broken RSA-2048 or the elliptic curves used online. The largest fault-tolerant benchmark we know of ran 8 logical qubits; RSA-2048 needs about 1,400.
Will Q-Day break all encryption? No. It breaks public-key cryptography (RSA, ECC). Symmetric encryption such as AES stays secure with large enough keys.
Is my Bitcoin at risk? Bitcoin uses elliptic-curve signatures, which Shor's algorithm breaks. How exposed a coin is depends on whether its public key is visible; see our Bitcoin explainer.
When should organizations act? Now. NIST advises starting the transition as soon as possible, and migrating large systems takes years.